
Secrets can be stored in Databricks Unity Catalog. Now what?
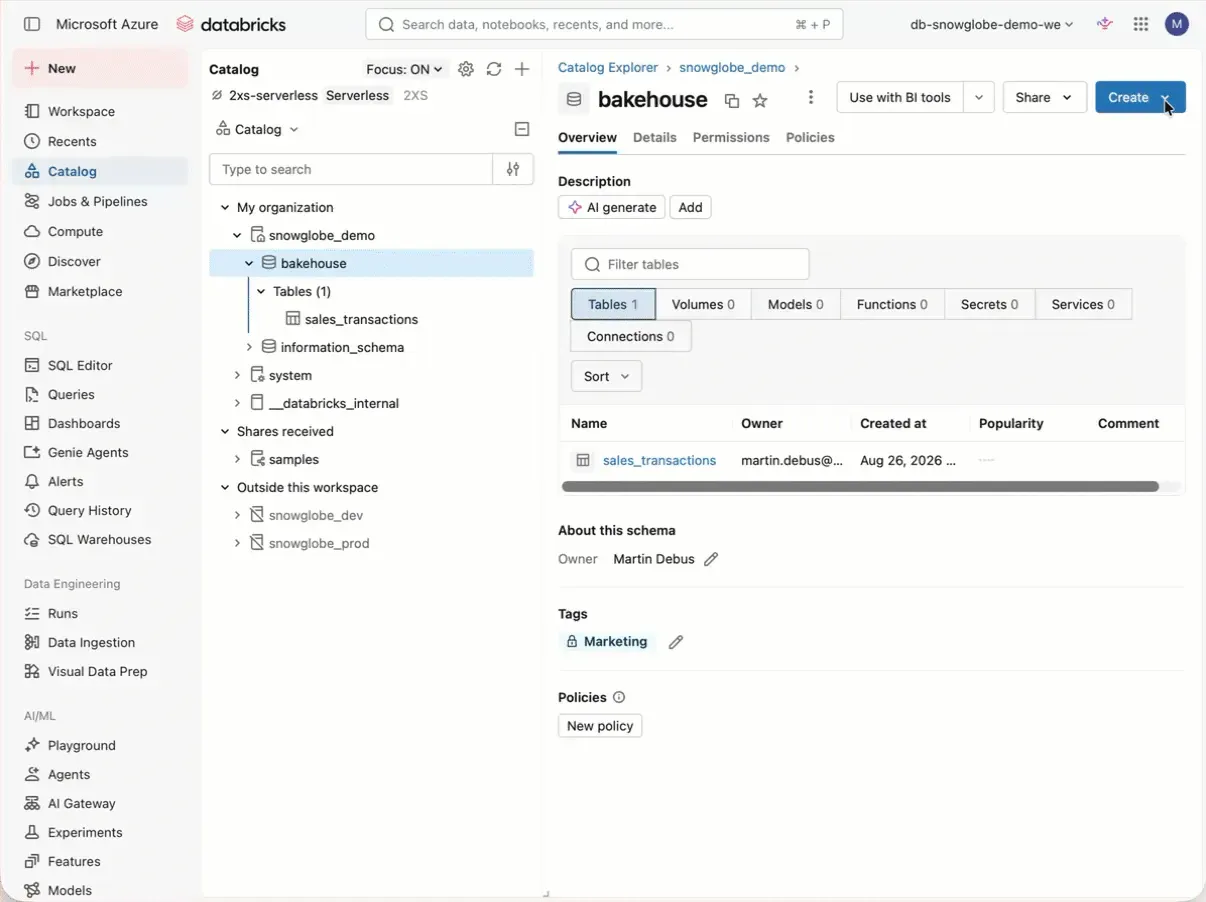
This feature has been GA (generally available) for a few weeks now. Compared to secret scopes, this adds a level of discoverability in the Catalog explorer. The secret value can be retrieved as usual using the dbutils command, but instead of referencing the secret scope, just use catalog, schema, and secret name to get it.
Some limitations apply yet, e.g. it runs only on Databricks Runtime 17.3 and higher, Serverless environment verstion 4+ and not on SQL Warehouses.
I wonder in what scenarios it makes sense to migrate existing secrets from a secret scope into Unity Catalog secrets. I could not find any guidelines in the documentation.
What is your opinion? Migrate or not? All or only some secrets that meet certain criteria?